
GitHub Actions Lockfiles Turn Workflow Tags Into Reproducible CI
GitHub Actions workflow lockfiles are now generally available. Here is what pinned commits, Dependabot updates, and the Require lockfile policy change for CI teams. Read More
Category
GitHub Actions workflow lockfiles are now generally available. Here is what pinned commits, Dependabot updates, and the Require lockfile policy change for CI teams. Read More
A new Canadian Cyber Centre alert on CVE-2026-111497 shows how a flaw in a compression decoder can spread through runtimes, proxies and applications that quietly depend on the same low-level library. Read More

CERT-In has published a high-severity advisory covering Apple platform vulnerabilities. The important detail is the version matrix: the same advisory spans browsers, operating systems, wearables, television and spatial-computing devices. Read More

Docker says Desktop 4.97.0 addresses credential exposure in local logs and a container-to-VM networking issue. The paired fixes show why desktop container security includes both diagnostic data and the virtualization boundary. Read More

Oracle has announced AI Security Mesh, a managed service that combines OpenAI cyber models with Oracle testing tools and controlled permissions. The important shift is from AI-generated findings to an evidence-backed, approval-driven remediation workflow. Read More
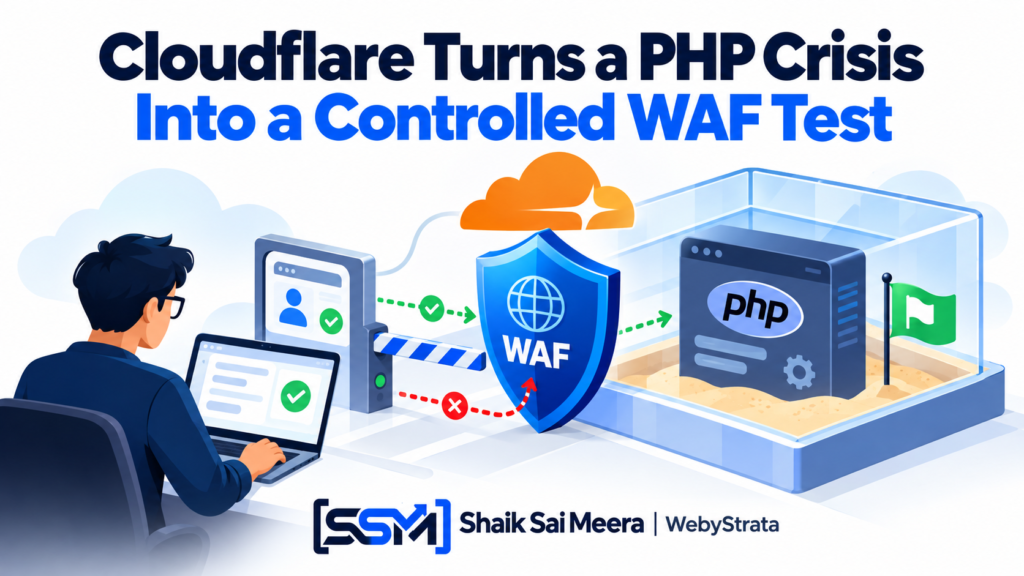
Cloudflare has launched a limited PHP Capture the Flag challenge behind its WAF. The experiment shows why defensive controls need realistic, authorized testing—and why a WAF is not a patch. Read More